
Market report
Fintech security and regulatory compliance best practices and checklists
Author
Published
Sep 4, 2024
Length
27 pages
Intro
Fintech companies are becoming subject to regulatory requirements like any other technology-led subjects that create regulatory issues.
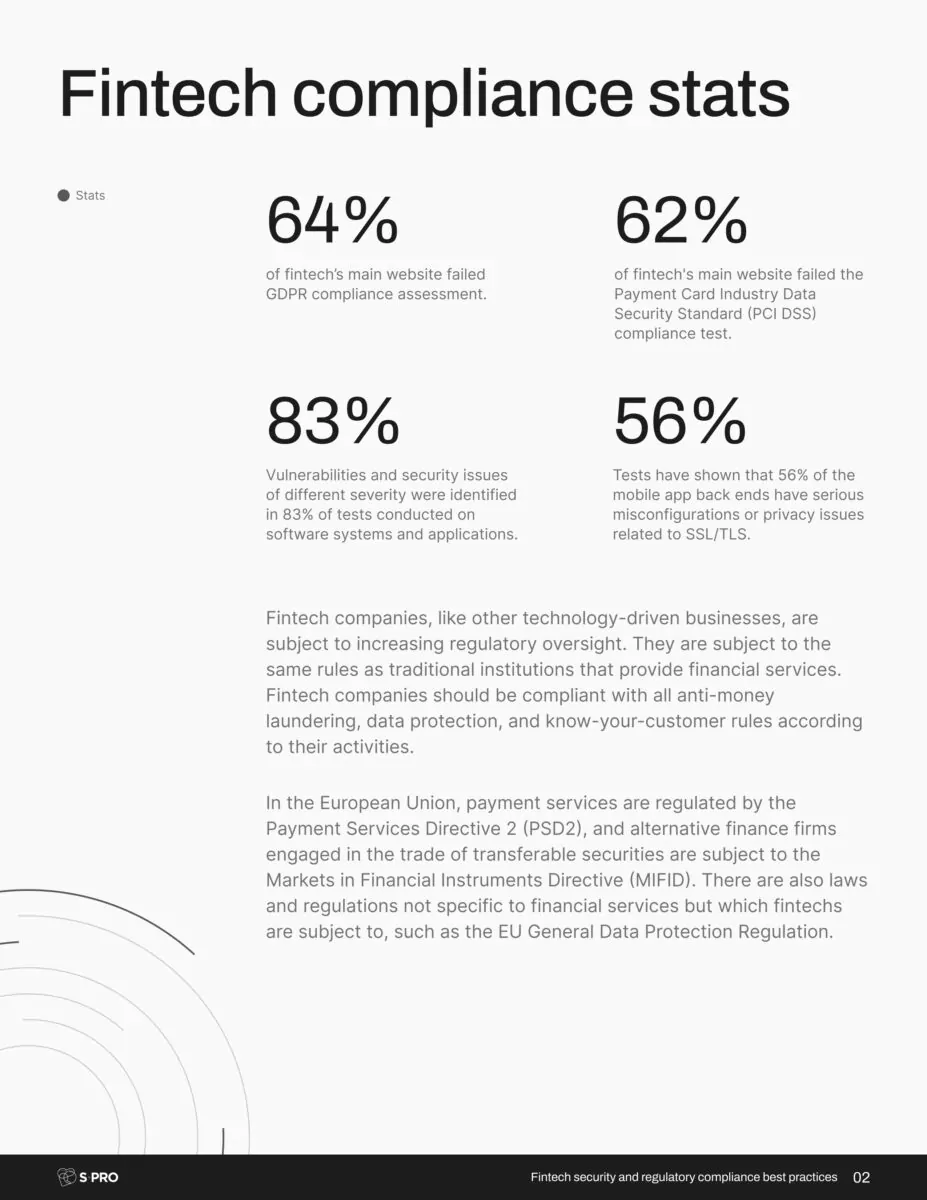
They are subject to the same rules as traditional institutions that provide financial services. Fintech companies should be compliant with all anti-money laundering, data protection, and know-your-customer rules according to their activities.
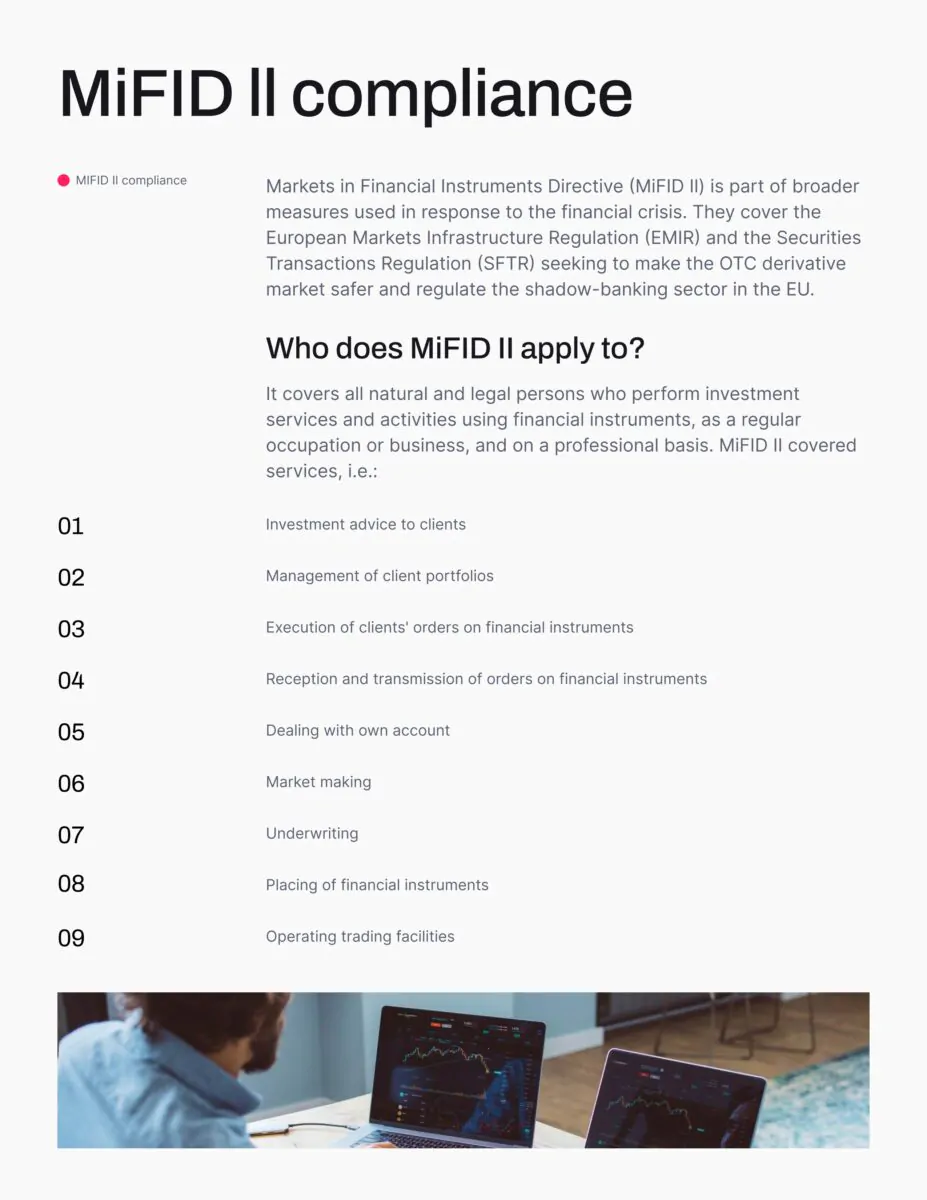
In the European Union, payment services are regulated by the Payment Services Directive 2 (PSD2), and alternative finance firms engaged in the trade of transferable securities are subject to the Markets in Financial Instruments Directive (MiFID).
There are also laws and regulations not specific to financial services but which Fintechs are subject to, such as the EU General Data Protection Regulation.
Key findings and insights from the market report
01
Fintech security fails
56% of the mobile app back ends have serious misconfigurations or privacy issues related to SSL/TLS.
02
Violation of PCI DSS standards
62% of Fintech’s main website failed the Payment Card Industry Data Security Standard (PCI DSS) compliance test.
03
GDPR compliance gap
64% of Fintech’s main website failed GDPR Compliance assessment.
What’s inside
Discover how to ensure compliance with security standards and align with best practices.
- Introduction
- Fintech compliance stats
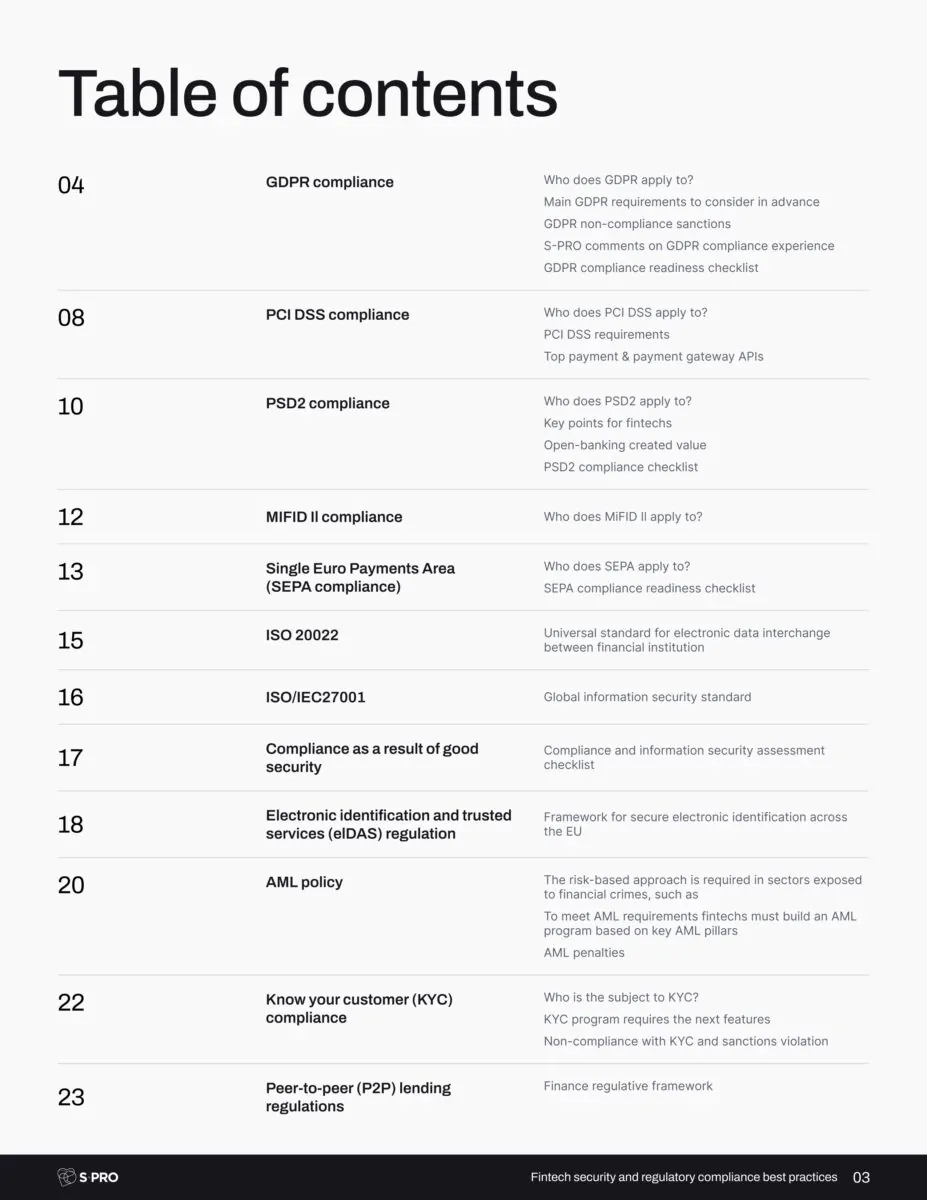
- Table of contents
- GDPR compliance
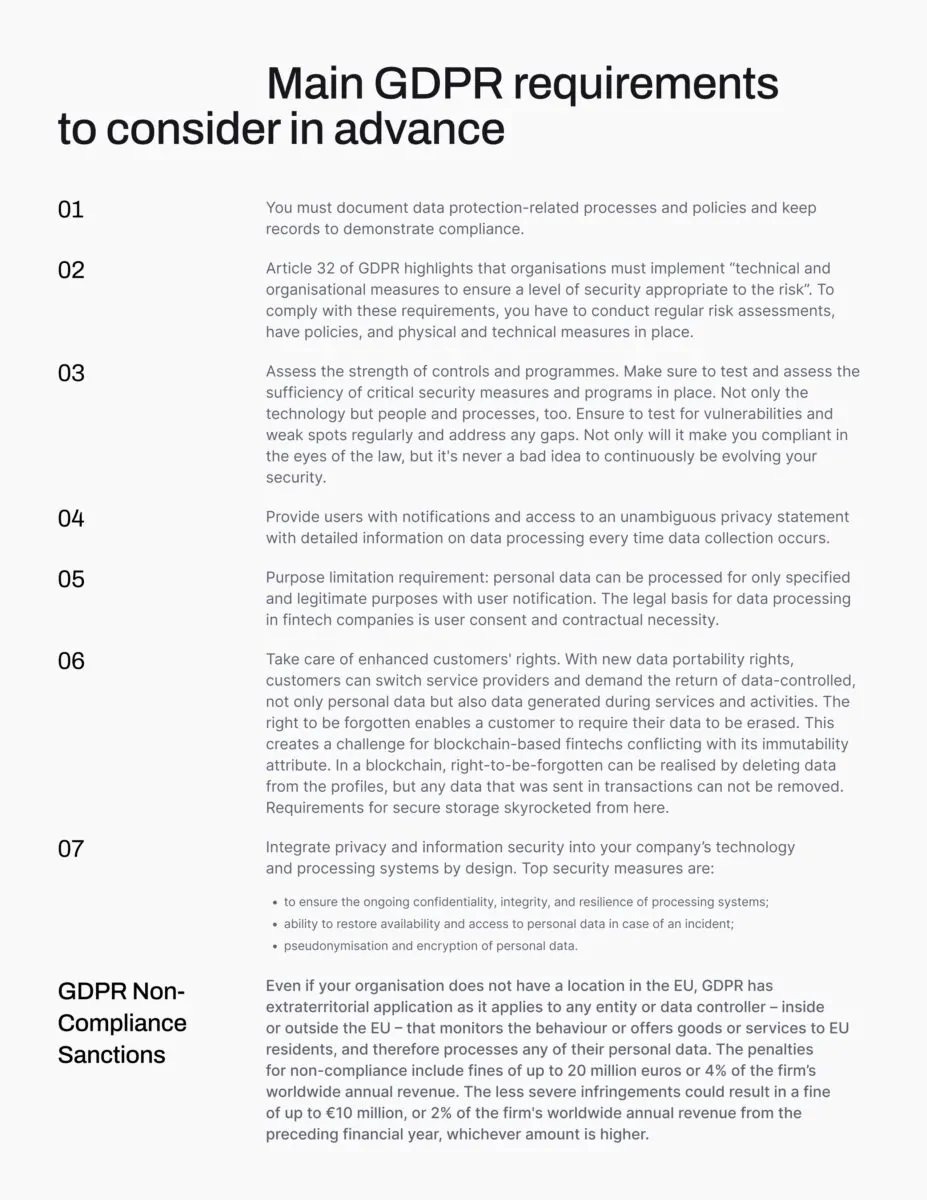
- Main GDPR requirements
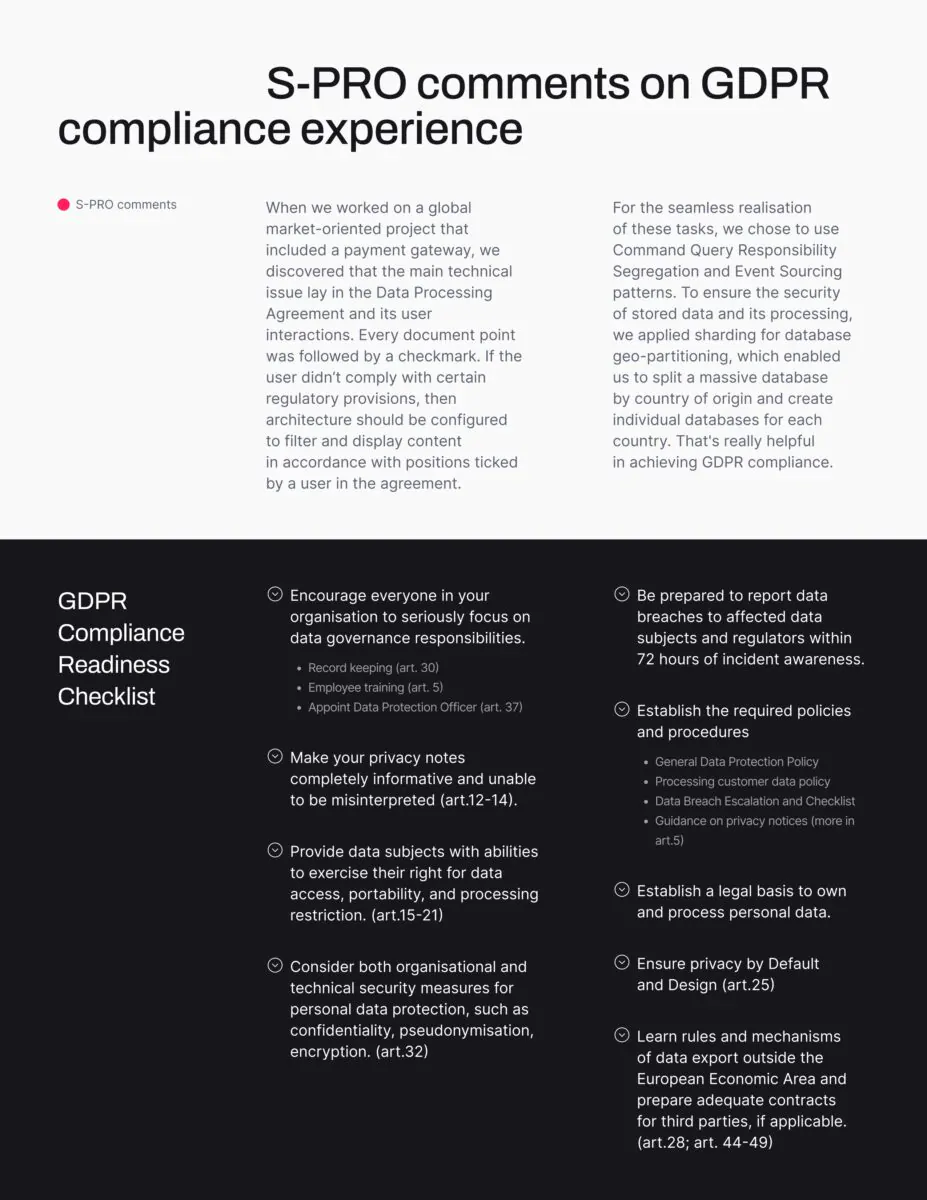
- S-PRO comments on GDPR
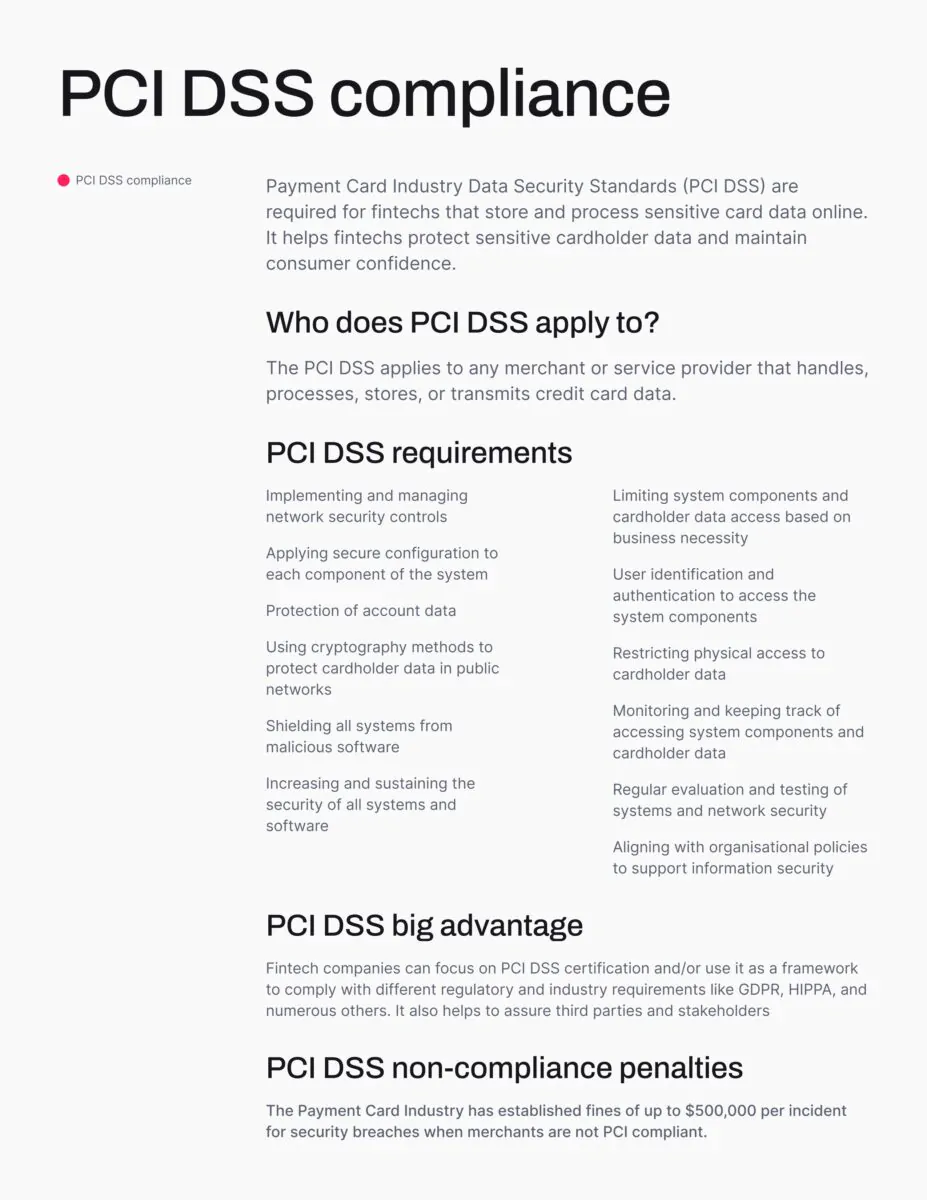
- PCI DSS compliance
- S-PRO comments on PCI DSS compliance
- Other important regulations
- PSD2 compliance
- PSD2 Compliance Checklist
- Checklist

1/12
Get a free copy
Download the market report
We will send you a full report to the email address you provided.

Thank you!
The report has been successfully sent. Please check your inbox.